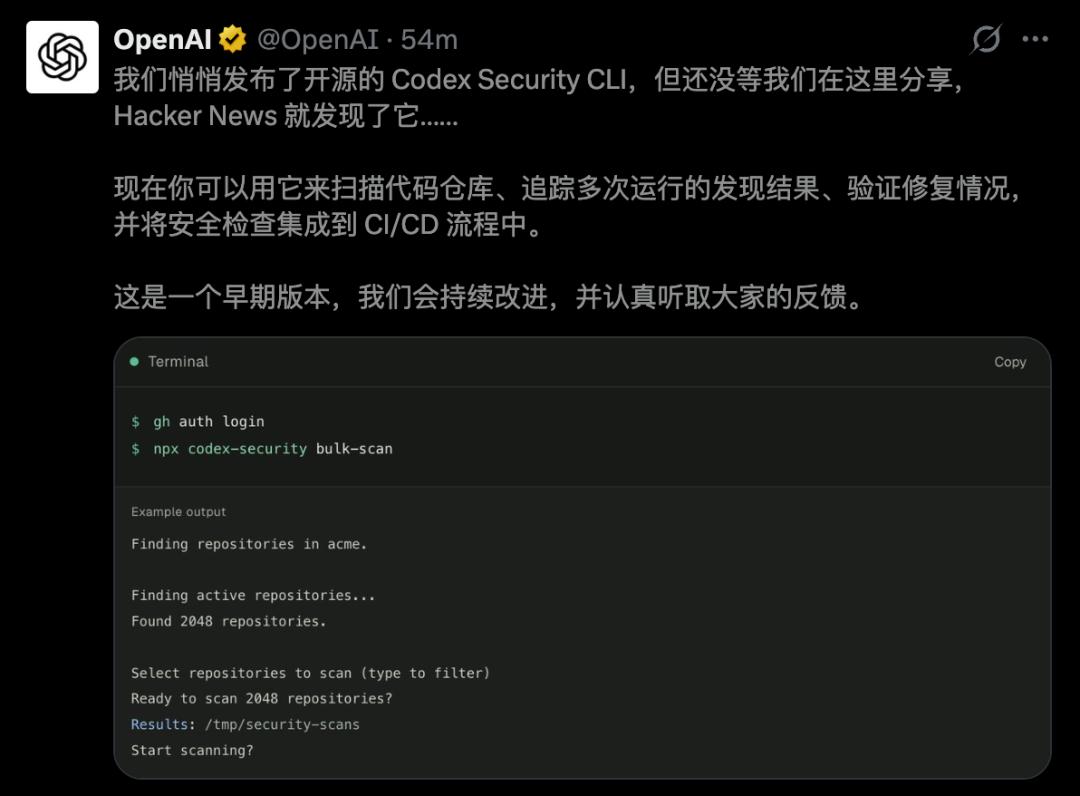
OpenAI官方宣布开源代码安全工具Codex Security CLI,这是一款能够自动发现、验证和修复代码漏洞的应用安全智能体1。该工具已在GitHub上线,地址为https://github.com/openai/codex-security[1](#source-1)。
上线后的前30天内,Codex Security CLI扫描了超过120万次提交,发现了792个严重级别漏洞和10561个高危级别漏洞1。不过,该工具的默认配置调用高成本的gpt-5.6-sol模型,推理强度设为extra-high,导致部分开发者遭遇账单超支的问题1。据悉,Sol模型API定价为每百万输入token 5美元、每百万输出token 30美元1。开发者gregwebs报告称,一次52分47秒的扫描耗尽了其Pro套餐周度额度的一半,另一名开发者Quai的一次失败运行则花费约13美元1。
Codex Security CLI脱胎于2025年10月的私测项目Aardvark,于今年3月6日推出研究预览版1。值得注意的是,对同一批代码仓库进行反复扫描时,工具的误报率下降超过50%1。
OpenAI has announced the open-source release of Codex Security CLI, an application security agent designed to automatically discover, verify, and fix code vulnerabilities 1. The tool is available on GitHub at https://github.com/openai/codex-security 1.
During its first 30 days in operation, Codex Security CLI scanned over 1.2 million commits and identified 792 critical-level vulnerabilities and 10,561 high-severity vulnerabilities 1. However, the tool's default use of the high-cost GPT-5.6-Sol model, configured with extra-high reasoning intensity, has resulted in unexpectedly large bills for some developers 1. The Sol model's API pricing is set at $5 per 1 million input tokens and $30 per 1 million output tokens 1.
Multiple developers have reported significant expenses from using the tool. Developer gregwebs found that a single 52-minute, 47-second scan consumed half of his Pro subscription's weekly token allowance, while developer Quai reported that a failed scan attempt cost approximately $13 1. The project evolved from a private testing initiative called Aardvark that began in October 2025, before transitioning to a research preview version on March 6 1. Notably, repeated scanning of the same repository resulted in false positive rates dropping by over 50 percent 1.
评论
还没有评论,欢迎留下第一条。